AISystemsGovernance
BuilttoWithstandScrutiny.
Revoya helps security, compliance, risk, and operations leaders build the governance, controls, and operating systems required to adopt AI responsibly and at scale.
AI is moving faster than governance.
01
Shadow AI is expanding.
Employees are deploying AI tools outside IT and compliance oversight. Most organizations have no visibility into what is running.
02
Regulations are tightening.
The EU AI Act carries real penalties for organizations that are not prepared, and NIST AI RMF and ISO 42001 define what a defensible AI governance program looks like.
03
The governance gap is growing.
Most organizations have no AI policies, no accountability structures, and no framework for managing AI risk at scale.
Our Approach
How we make governance real.
We identify every AI system across your organization, including the ones nobody registered. We map each system to its risk level, data classification, and regulatory exposure.
We build the policies, frameworks, and controls your organization needs to manage AI responsibly, including data governance policies that govern how AI systems access, use, and retain data across your environment. Aligned to the EU AI Act, NIST AI RMF, ISO 42001, and your industry-specific requirements. Not a binder on a shelf. Governance your teams actually follow.
We run your AI governance program so you do not have to build a team from scratch. Ongoing monitoring, compliance reporting, audit preparation, and board-ready reporting.
Our Services
Assess. Build. Operate.
Three core engagements that take you from unknown AI exposure to a governance program that runs.
Assess
“We need to understand our exposure.”
AI Governance Readiness Assessment
Know where your AI exposure is, what needs to be fixed first, and what governance needs to be built.
See what you receiveBuild
“We need an actual governance program.”
AI Governance Program Build
A functioning AI governance program your organization can operate: operating model, policies, controls, and reporting.
See what you receiveOperate
“We need someone to run this with us.”
Managed AI Governance
Ongoing AI governance without building a full internal function. We run the recurring work with your team.
See what you receiveSpecialist Engagements
Focused work for a specific decision or risk.
Specialist Engagement
“We need to evaluate this AI vendor.”
Vendor AI Risk Assessment
We evaluate the AI risk a vendor introduces before you sign, renew, or expand the relationship.
See what you receiveSpecialist Engagement
“Our workforce is using AI and we need structure.”
Governed AI Adoption Program
Move employees from unmanaged AI experimentation to approved, measurable, and governed AI use.
See what you receiveSpecialist Engagement
“We are deploying agents and need governance before production.”
AI Agent Governance & Deployment Review
Your engineering team builds the agent. Revoya governs the implementation so it is ready for production.
See what you receiveFree Resource
Assess where your organization stands across five governance domains
Used by compliance and GRC leaders to baseline AI risk posture and prioritize remediation.
What's inside
- Five-domain maturity model covering governance structure, policy, risk, vendor controls, and monitoring
- Scoring rubric to identify your current maturity level and gap areas
- Prioritized remediation guidance mapped to NIST AI RMF and ISO 42001
- Executive summary template for board and audit committee reporting
No credit card required. Delivered to your work inbox instantly.
Industries Served
Built for regulated industries.
Why Revoya
Governance experience that organizations trust.
14+
Years of enterprise GRC experience
3
Frameworks: EU AI Act, NIST AI RMF, ISO 42001
6
Regulated industries served
Built on deep organizational governance, risk, and compliance experience across financial services, healthcare, manufacturing, and technology. We bring the frameworks, the expertise, and the operational rigor to make AI governance real.
As organizations integrate AI into critical workflows, data governance has become the first question every security and compliance leader asks. We answer it.
How It Works
Simple steps to get started.
01
Discovery Call
30-minute conversation to understand your AI landscape and assess fit.
02
Proposal
Tailored engagement plan delivered in 48 hours.
03
Kickoff
Meet your dedicated team and begin immediately.
04
Deliver & Operate
Assessments, policies, monitoring, and ongoing strategic support.
Next Step
Ready to govern AI responsibly?
Request a complimentary 30-minute consultation.
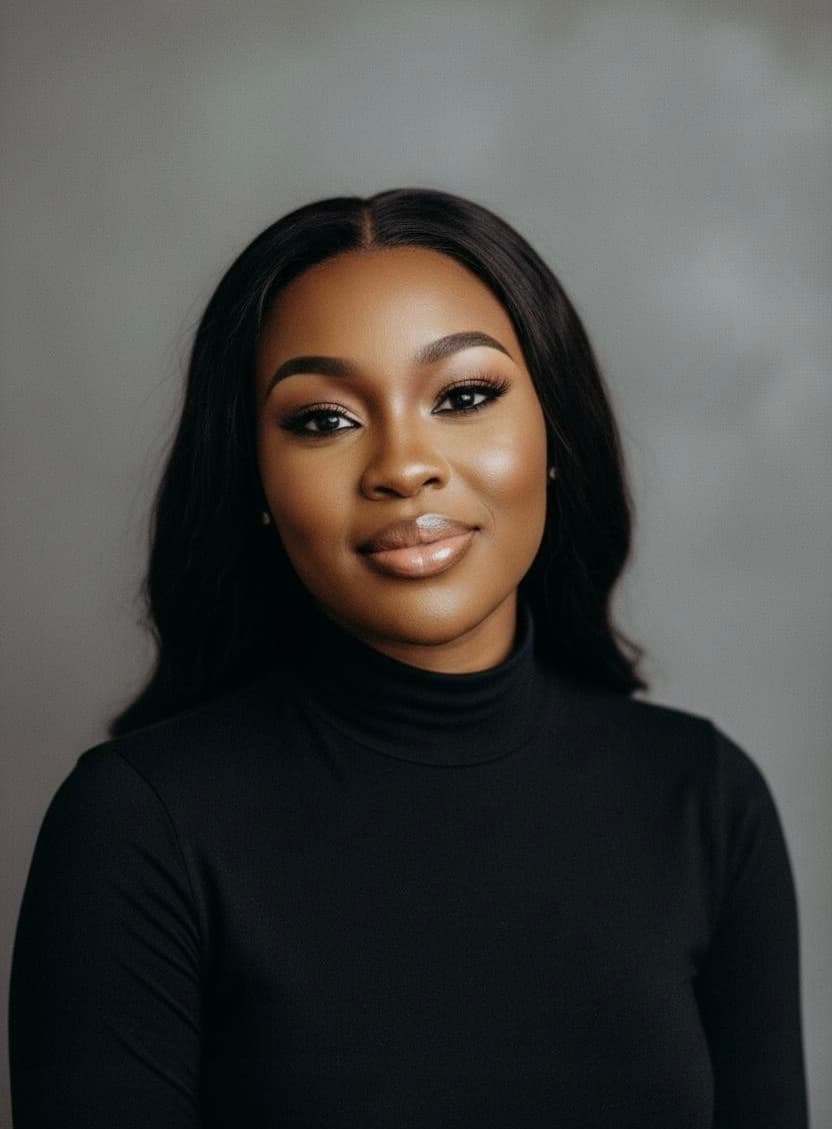
The Founder
Mary Ajayi founded Revoya to help organizations adopt and scale AI with the governance, controls, and operating discipline expected in complex enterprises. She brings more than 14 years of experience across governance, risk, compliance, cybersecurity, and technology in highly regulated industries, including financial services, healthcare, technology, and manufacturing. Her experience includes building enterprise GRC programs from the ground up and translating complex risk requirements into practical systems organizations can operate at scale.